Deploy Nebari on Azure
Introduction
Section titled “Introduction”This guide is to help first-time users set up an Azure account specifically for the purpose of using and deploying Nebari at a production scale. In this guide we will walk you through the following steps:
- Introduction
- Sign up for Azure
- Authentication
- Initializing Nebari
- Deploying Nebari
- Destroying Nebari
For those already familiar to Azure subscriptions and infrastructure services, feel free to skip this first step and jump straight to the Nebari authentication section of this guide.
Sign up for Azure
Section titled “Sign up for Azure”This documentation assumes that you are already familiar with Azure accounts and subscriptions, and that you have prior knowledge regarding Azure billing and cost usage for Kubernetes related services.
If you are new to Azure, we advise you to first sign up for a free account to get a better understanding of the platform and its features. Billing for Azure services is done on a per-subscription basis. For a list of the available subscription offers by type, see Microsoft Azure Offer Details and Azure Kubernetes Service for a quick overview of the Kubernetes services.
Refer to our Conceptual guides for more information regarding the basic infrastructure provided by Nebari.
Authentication
Section titled “Authentication”In order for Nebari to make requests against the Azure API and create its infrastructure, an authentication method with the appropriate permissions will be required. The easiest way to do this is using a service principal with suitable permissions for your Azure subscription.
There are three tasks necessary to create a Service Principal using the Azure Portal:
- Create an Application in Azure Active Directory, which will create an associated Service Principal;
- Generating a Client Secret for the Azure Active Directory Application, which Nebari will use to authenticate;
- Grant the Service Principal access to manage resources in your Azure subscriptions
If it's your first time creating a service principal account, please refer to these detailed instructions to create a service principal for more information on how to create an Azure service principal with necessary level permissions over the Azure subscription.
By default, Nebari will try to use the credentials associated with the current Azure infrastructure/environment for authentication. Keep in mind that Nebari will only use these credentials to create the first roles and stricter permissions for Nebari's internal components. Refer to [Conceptual guides] for more information on how Nebari's components are secured.
As we've obtained the credentials for the Service Principal, provide authentication credentials to Nebari by setting the following environment variables:
export ARM_CLIENT_ID="" # application (client) IDexport ARM_CLIENT_SECRET="" # client's secretexport ARM_SUBSCRIPTION_ID="" # Available at the `Subscription` section under the `Overview` tabexport ARM_TENANT_ID="" # Available under `Azure Active Directories`>`Properties`>`Tenant ID`Initializing Nebari
Section titled “Initializing Nebari”Great, you’ve gone through the Nebari Installation and authentication setup steps, and have ensured that all the necessary environment variables have been properly set.
In this step, you'll run nebari init to create the nebari-config.yaml file.
-
In your terminal, start by creating a new project folder. For this demonstration, we will name the new folder
nebari-azure:Terminal window mkdir nebari-azure && cd nebari-azure -
Executing the
nebari init --guided-initcommand prompts you to respond to a set of questions, which will be used to generate thenebari-config.yamlfile with the Nebari cluster deployed on Azure.
nebari init --guided-init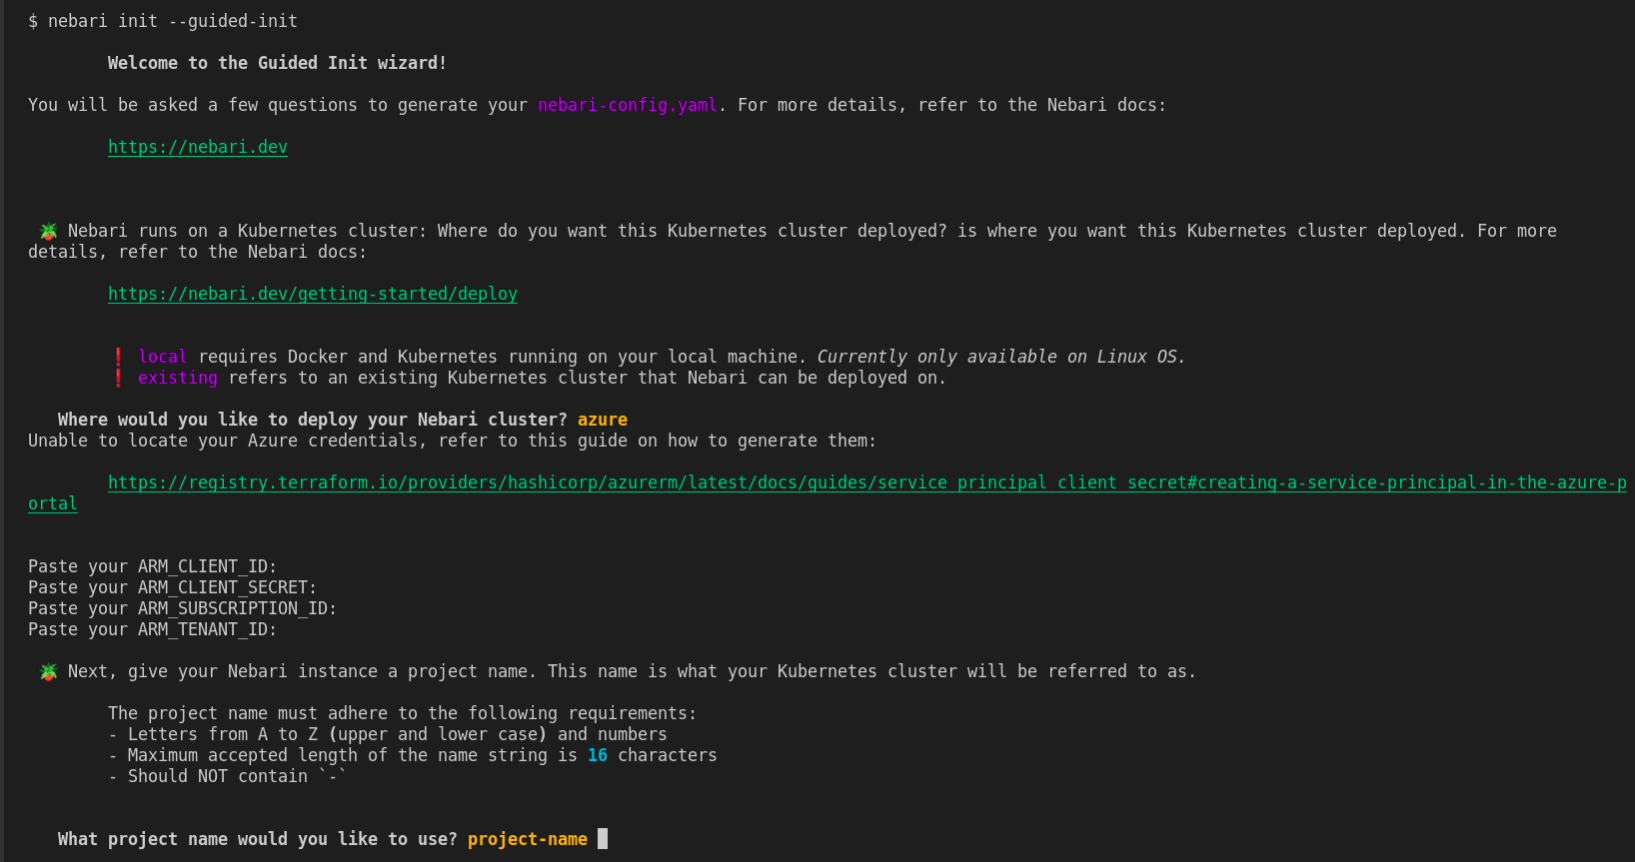
Once nebari init is executed, you should then be able to see the following output:
Securely generated default random password=*** for Keycloak root user stored at path=/tmp/QHUB_DEFAULT_PASSWORDCongratulations, you have generated the all important nebari-config.yaml file 🎉
You can always make changes to your nebari-config.yaml file by editing the file directly.If you do make changes to it you can ensure its still a valid configuration by running:
                nebari validate --config path/to/nebari-config.yaml
For reference, if the previous Guided Init answers were converted into a direct nebari init command, it would be:
               nebari init <cloud-provider> --project-name <project-name> --domain-name <domain-name> --namespace dev --auth-provider password
You can now deploy your Nebari instance with:
        nebari deploy -c nebari-config.yaml
For more information, run nebari deploy --help or check out the documentation: https://www.nebari.dev/how-tos/You can see that Nebari is generating a random password for the root user of Keycloak. This password is stored in a temporary file and will be used to authenticate to the Keycloak server once Nebari's infrastructure is fully deployed, in order to create the first user accounts for administrator(s).
The Nebari initialization scripts create a nebari-config.yaml file that contains a collection of default preferences and settings for your deployment.
The generated nebari-config.yaml is the configuration file that will determine how the cloud infrastructure and Nebari is built and deployed in the next step.
Since it is a plain text file, you can edit it manually if you are unhappy with the choices you made during initialization, or delete it and start over again by re-running nebari init.
Deploying Nebari
Section titled “Deploying Nebari”To see all the options available for the deploy command, run the following command:
nebari deploy --help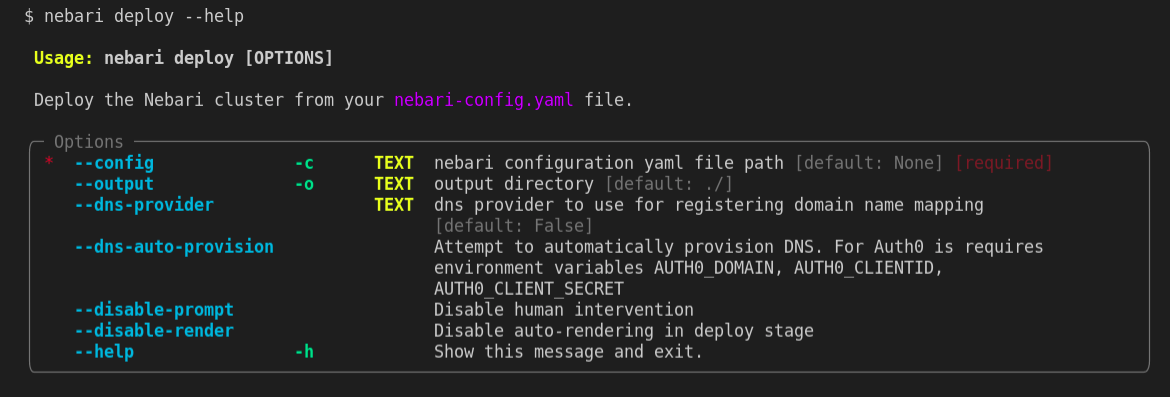
With the nebari-config.yaml configuration file now created, Nebari can be deployed for the first time. Type the following command on your command line:
nebari deploy -c nebari-config.yamlThe terminal will prompt you to press enter to check the authentication credentials that were added as part of the preceding nebari init command. Once Nebari is
authenticated, it will start its infrastructure deployment process, which will take a few minutes to complete.
If the deployment is successful, you will see the following output:
[terraform]: Nebari deployed successfullyServices: - argo-workflows -> https://projectname.domain/argo/ - conda_store -> https://projectname.domain/conda-store/ - dask_gateway -> https://projectname.domain/gateway/ - jupyterhub -> https://projectname.domain/ - keycloak -> https://projectname.domain/auth/ - monitoring -> https://projectname.domain/monitoring/Kubernetes kubeconfig located at file:///tmp/NEBARI_KUBECONFIGKubecloak master realm username=root *****...Congratulations! You have successfully deployed Nebari on Azure! From here, see Initial Nebari Configuration for instructions on the first steps you should take to prepare your Nebari instance for your team's use.
Destroying Nebari
Section titled “Destroying Nebari”To see all the options available for the destroy command, type the following command on your command line:
nebari destroy --help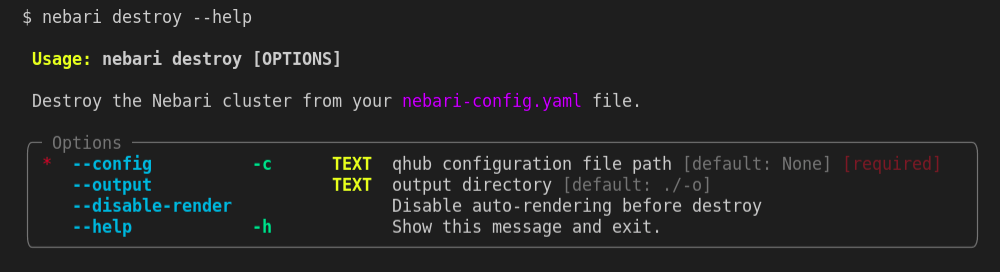
Nebari also has a destroy command that works the same way the deploy works but instead of creating the provisioned resources it destroys it.
nebari destroy -c nebari-config.yaml